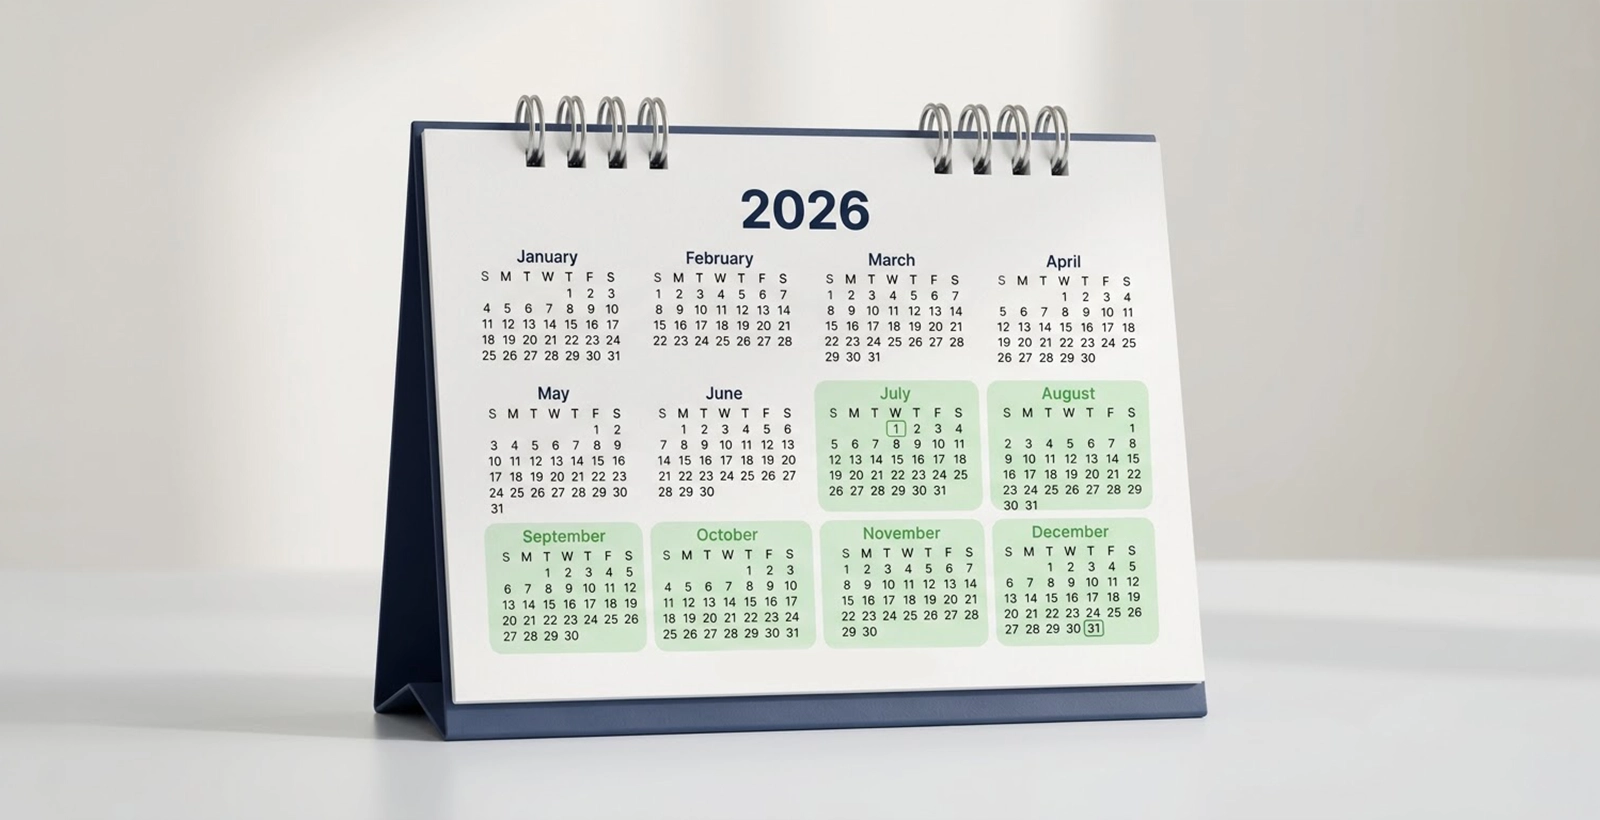
The deadline for the SWIFT CSP attestation is no mere ‘soft target,’ but a hard deadline with real penalties for non-compliant financial organizations. All SWIFT-participating entities, from multinational correspondent banks to regional payment processors, must deliver an attestation that meets the compliance standards via the KYC Security Attestation portal by 31 December, and the period within which such submission is possible opens on 1 July.
Compliance managers, or CISOs, responsible for this task have a six-month window to deal with everything, but it is easy to run out of time when all of this takes much preparation and planning. Organizations which view 1 July as the beginning, not the preparation phase, end up doing much of their work in the last weeks of the fourth quarter – the moment when mistakes happen, gaps in security are ignored and submitted attestation doesn’t actually represent the current state of things.
In this blog post we explain what the SWIFT CSP attestation is, to whom does it apply, what does the current framework require, and how to prepare so that your attestation submission would be truthful to the current state of things.
SWIFT CSP (Customer Security Programme): This is a mandatory security programme introduced by SWIFT in 2016, whereby all institutions using the network will have to ensure they comply with a specific list of security controls that will safeguard the global interbank messaging environment against any fraud or compromise.
CSCF (Customer Security Controls Framework): This is the document that sets out the security controls an institution is required to assess in order to pass attestation for the year in question. The CSCF is updated on a yearly basis; therefore, an organisation must assess the current CSCF version in order to pass attestation.
KYC-SA (Know Your Customer – Security Attestation) Portal: This is the SWIFT-managed portal used by member institutions to submit their yearly attestation, check compliance with counterparts, and keep security attestation records.
Independent Assessment: An external assessment performed by an independent evaluator on the SWIFT environment of an institution, used to verify that self-assessed controls are being adhered to. Independent assessment is required for some institutions, while others are strongly encouraged to obtain an independent assessment.
What SWIFT Attestation Services Actually Cover?
SWIFT attestation services provide the structured expertise, tooling, and independent assessment capability that financial institutions need to assess their SWIFT environment against the CSCF, remediate identified gaps, and submit a credible, evidence-backed attestation before the December deadline.
It is important to be clear about the meaning of “attestation services” in practice, because it is quite a loose term in use. First of all, SWIFT attestation services consist of two separate stages. The first stage is a readiness assessment. This is a comprehensive check of your SWIFT architecture against mandatory and recommended controls of the current CSCF version. These controls relate to your SWIFT local zone architecture, access management, endpoint security, software integrity verification and anomaly detection, among many others. As a result, you get a gap register, showing you what controls of the standard your environment already implements and where there is some remediation needed.
The second stage is attestation submission. It implies compilation of evidences, completion of the self-assessment questionnaire in the KYC-SA portal and, in case of an independent assessment being required or chosen, coordination with a qualified assessor who will verify your assessment. For large banks with complicated or geographically distributed SWIFT architecture, this stage alone is not easy to complete. It requires proper mapping of your architecture and coverage of all necessary components of the SWIFT environment in scope, as well as documenting all controls declared as compliant.
Why the Service Scope Matters for Compliance Officers?
Compliance officers often encounter a gap between what their internal teams can deliver and what the CSCF requires. Internal assessments conducted without structured methodology frequently miss edge cases — legacy interfaces operating outside the primary SWIFT zone, shared infrastructure components that cross the boundary of the defined secure zone, or software versions that no longer meet the mandatory baseline. A qualified SWIFT attestation services partner brings both the methodology and the institutional knowledge of how SWIFT’s controls apply to specific architecture patterns.
The difference between advisory and mandatory controls is another aspect wherein expert knowledge can prove helpful. Each version of CSCF brings some set of controls previously classified as advisory into the category of mandatory controls. Without being well acquainted with the history of the versions and the documentation provided by SWIFT, organizations might be unaware of the fact that they are attesting to compliance with obsolete controls.
How to Structure Your SWIFT CSP Attestation Preparation?
The most common mistake organisations make is conflating the attestation window with the preparation period. The window 1 July to 31 December is the submission period. It is not the time to begin understanding what the CSCF requires or to start assessing your environment for the first time. By the time 1 July arrives, an organisation with a well-run programme will have already completed its gap assessment, addressed the highest-priority control deficiencies, and assembled its evidence library. The window itself should be reserved for any final remediation, independent assessor engagement, and the submission process.

Phase One: CSCF Version Review and Scoping
The first step in any preparation programme is confirming which version of the CSCF applies to your current attestation cycle and identifying which controls have changed status since your last submission. SWIFT publishes CSCF updates in advance of each attestation year, and these updates are not always limited to minor clarifications.
The implementation of the changes necessary for mandatory controls can involve significant efforts including modifying existing infrastructures or implementing tools or processes, all of which take time.
Scoping is also important and is often overlooked. Your SWIFT secure zone the perimeter in which you have to apply the CSCF controls should be defined first before you start an assessment. Incorrect scoping, which may occur as a result of defining your perimeter either too narrowly or too widely can affect the whole assessment process negatively.
Phase Two: Gap Assessment and Remediation
Once your scoping is confirmed and the applicable CSCF controls are determined, a systematic gap assessment will compare your implementations against the controls. This is where an evidence-based approach will help you. The assessment should be based on your configuration records, access logs, scan results, and procedures rather than group consensus. Controls assessed without evidence cannot be defended in the event of an independent review challenge or regulatory enquiry.
Remediation should always be done in a risk-based manner. The mandatory requirements that have yet to be implemented present the greatest risks and should therefore be sorted out first prior to attestation. The advisory requirements, even though not mandatory for compliance, indicate new issues that SWIFT may consider making mandatory in future cycles. Tackling these now as part of a pre-planned program is much more effective than waiting for future cycles.
Phase Three: Evidence Compilation and Independent Assessment
This third phase of the preparation work is where you pull together all the evidence collected during the gap analysis phase and create a library for each attested control. The importance of having a good evidence library here is twofold – not only does it serve as your basis of documentation for your KYC-SA attestation, but this will also be the first line of defense if ever your attestation is disputed by one of your counterparties, correspondent banks or regulatory bodies. As you can see, the quality of this evidence library will be key when the independent reviewers review your attestation.
For firms that are opting to hire an independent assessor, the hiring process needs to happen much earlier than December, since the engagement process will take some weeks. Demand for independent reviews usually peaks at late Q3, since that is the time other firms in the same industry are meeting their December deadline as well.
Understand the Consequences of Non-Compliance
Consequences of non-compliance with the attestation are not theoretical. The KYC-SA portal is a live, counterparty-visible platform. The correspondent banks, the liquidity partners, and the clearing agents themselves constantly monitor the attestation status of their counterparties. The fact that an institution turns out to be non-compliant or overdue is an indication that risk management discussions are imminent, and in certain situations, that correspondent relationship itself needs to be reevaluated.
Beyond counterparty visibility, SWIFT has established a framework under which persistent non-compliance is escalated to local supervisory authorities. This supervisory notification mechanism means that non-compliance does not remain a private matter between the institution and SWIFT. Regulators who receive these notifications may initiate their own enquiries, particularly in jurisdictions where SWIFT security compliance has been incorporated into broader cybersecurity or operational resilience regulatory expectations.
The Reputational Dimension
It is worth acknowledging the reputational dimension of attestation compliance, because it operates differently from other regulatory requirements. Unlike a regulatory examination or audit finding which may remain confidential attestation status on the KYC-SA portal is observable by the broader network of an institution’s counterparties. A pattern of late or qualified attestations signals a maturity gap in cybersecurity governance that sophisticated counterparties take seriously. For institutions seeking to establish new correspondent relationships or enter new payment corridors, a clean, timely attestation record is a baseline expectation, not a differentiator.
This is why organisations that invest in structured SWIFT CSP attestation preparation services are not simply managing a compliance checkbox. They are actively protecting the trust infrastructure that underpins their ability to operate within the global interbank network.
Conclusion
The SWIFT CSP attestation window is open, and time is ticking. For compliance officers and CISOs, the timeframe from now until 31 December is not the time to start working out what the framework means but the time to finalize your assessment results, fill in any gaps in your remediations, work with independent assessors where needed, and make sure your attestation tells the true story about the security status of your SWIFT environment. The institutions who always get their clean, timely attestations are those who have prepared for it as an ongoing process.
The SWIFT CSP attestation process is an annual mandatory compliance activity that involves the submission of a compliance statement regarding the CSCF through the KYC-SA portal, between 1 July and 31 December. Preparing properly by ensuring you review CSCF version; scope your environment; assess and remediate any control gaps; compile evidence – should be something you do long before the attestation window opens. Failure to comply results in counterparty visible status changes, notifications to regulators and possible damage to your reputation in the correspondent banking world. Your SWIFT CSP attestation deadline is fixed your preparation timeline is not. If your team is working through a gap assessment, navigating the updated CSCF controls, or evaluating whether independent assessment is required for your institution, ValueMentor is ready to support you. Visit our website to learn how our SWIFT attestation services can help you submit with confidence before 31 December.
FAQs
SWIFT CSP attestation is the formal annual process through which SWIFT member institutions confirm compliance with the Customer Security Programme controls. Organisations must assess their SWIFT-connected infrastructure against mandatory and advisory security controls and submit a verified compliance statement through the KYC Security Attestation portal by 31 December each year.
2) Who is required to complete SWIFT CSP attestation?
All entities connected to the SWIFT network must complete CSP attestation annually. This obligation applies to banks, payment processors, broker-dealers, custodians, and any financial institution operating a SWIFT interface — regardless of transaction volume or the size of their SWIFT footprint. There are no exemptions based on organisational scale.
3) What happens if you fail SWIFT CSP attestation?
Non-compliant or overdue attestation status becomes visible to counterparties through the KYC-SA portal and triggers supervisory notification to the institution’s local financial regulator. Persistent non-compliance can result in restricted network access and reputational consequences with correspondent banking partners who review attestation records before establishing or renewing relationships.
4) How often must SWIFT CSP attestation be completed?
The SWIFT CSP attestation needs to be done every year. The window period starts on 1st July and ends on 31st December. As SWIFT CSP updates the Customer Security Control Framework every year, there may be some changes to the requirements during each cycle, which need to be assessed by the organisation.